Just a guy in Vermont trying to connect all the dots...

Dan York
Author's posts
Nov 26
New Github repo for using WordPress with Docker
As I wrote over on my Disruptive Conversations site, I’ve been playing around with using Docker as a way to easily test new WordPress versions and plugins. As part of that testing, I was trying to use the official WordPress image found on Dockerhub.
However, I was struggling with getting started, because the WordPress container is just… WordPress. It also needs a database to work, and my Docker experience was not yet strong enough to sort out how to link various containers together. So I raised an issue on Github asking about a step-by-step tutorial.
Github user wglambert very kindly provided a simple docker-compose.yaml file that could launch both WordPress and MySQL in separate containers and set up the necessary network and links.
It works wonderfully! And it has now been added to the instructions on DockerHub. (Thank you to the DockerHub admins for merging it in.)
Because I want to easily use the file on different systems, I put it up in a Github repo:
https://github.com/danyork/wordpress-basic-docker
Any of you are welcome to use it, too!
As I noted in my Disruptive Conversations article, I’m planning to start writing here a good bit more about using Docker. I’m rather impressed by all that can be done – and want to capture my own experiments here for my own future knowledge… and if it helps any of you all out, too, all the better!
Nov 26
How to Run WordPress in a Docker Container, Part 1
Here is a quick 3-step process for launching WordPress in a Docker container. You can use this to easily launch a new WordPress instance on your local system to test out new versions, new plugins or anything else.
First, though, you need to have Docker installed on your system. The simplest way for Mac and Windows users is to install Docker Desktop. This desktop download also gives you Docker Compose, which you will need. If you are running Docker on a Linux system, you will need to manually install Docker and Docker Compose.
To run WordPress, you also need a database running. The steps here use Docker Compose to launch TWO containers: one for WordPress and one for MySQL.
Three steps
Step 1 - Create a directory (a.k.a. "folder") and install the docker-compose.yaml file found in this Github repository. You can get the file three ways:
- using git:
git clone https://github.com/danyork/wordpress-basic-docker.git - direct download: https://raw.githubusercontent.com/danyork/wordpress-basic-docker/master/docker-compose.yaml
- copy / paste the text into your own file named
docker-compose.yaml
The key is to have this all in a separate directory because your WordPress installation will store some plugins there (see the notes below).
Step 2 - In a terminal window[1] type 'docker-compose up’
This will launch the two containers and link them together. You will see logging to your terminal window. You can press Ctrl+C to stop the containers and get your command prompt back. To launch the containers in the background add a "-d" option:
docker-compose up -d
Step 3 - Connect to your new WordPress server at http://localhost:8080/
That's it!
Now you simply go through the normal WordPress installation process and within a few screens your new site will be fully active.
Next you can update WordPress to the latest version, install whatever plugins you want, etc.
For example, I installed the WordPress Beta Tester plugin, went into its settings and turned on "Bleeding edge nightlies", performed an upgrade... and now I'm running the very latest WordPress 5.0 build. Perfect for the testing I want to do.
Credit for the simplicity of this approach is due to Github user "wglambert" who answered a request I made about help using the WordPress Docker container. Thank you!
Notes
- Stopping the containers - do '
docker-compose stop'. This will stop the containers from running. Doing 'docker-compose start' will start them up again. - A '
wp-content' directory is created is created inside the directory in which you put the docker-compose.yaml file. Any plugins or themes you add will be stored here. This allows you to do a reinstallation and have all the plugins and themes available. - WHEN YOU ARE DONE and want all this to go away, just type '
docker-compose down' and the services will be stopped and the containers removed.
There are many more things you can do with docker-compose. The command-line documentation can help you learn more.
Next parts
I labeled this as "Part 1" because I'm planning to write about my own ongoing testing with Docker and WordPress. In future parts of this series, I intend to cover:
- How to load in an existing site for testing
- How to save your changes in a Dockerfile (so you don't have to start at the very basic installation each time)
- ... and other things I learn along the way.
I also expect I may update THIS article over time as I do more with using WordPress and Docker.
I hope you found this helpful. Please feel free to leave comments here (unfortunately I have to moderate due to spam, and so comments will not appear immediately).
I also welcome pointers to other "WordPress and Docker" tutorials that people have found helpful. If you want to follow along with some of my other experiments with Docker and containers in general, I'll be writing about that over on Code.DanYork.com.
[1] or "command shell" or "powershell" or whatever you call it...
Nov 21
Watching the spammers invade Known

It's been over 3 years since I last posted here on Known. I had in fact not thought much about this site.
UNTIL... about 5 days ago when I started getting notifications about comments being added to various posts here.
Yep, the spammers are here. Maybe they have been for a while and just hadn't yet targeted my posts. But now they have.
Rather ironically, they were posting spam comments on a post I wrote in 2014 about Webmentions and the possibility of spam.
Obviously that is still an issue. :-(
This is why we can't have nice things.
Nov 02
TDYR 358 – Heading to Bangkok for IETF 103
I am on my way to Bangkok, Thailand, for the 103rd meeting of the Internet Engineering Task Force (IETF). In this episode I explain why I am going...
Nov 02
Rough Guide to IETF 103: DNSSEC, DNS Security and DNS Privacy
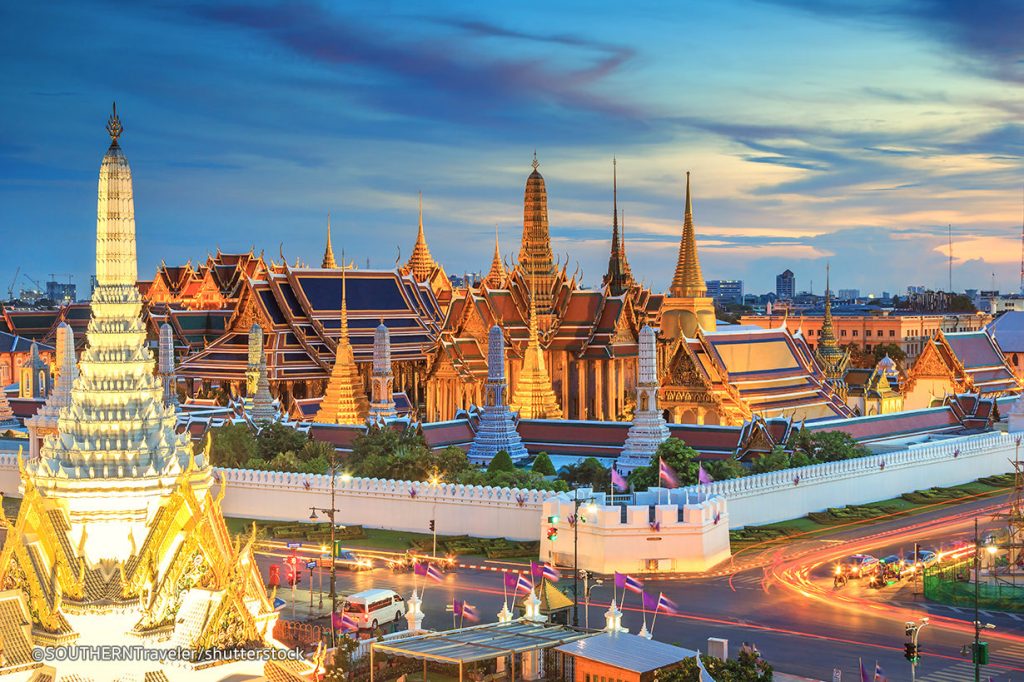
As happened earlier this year at IETF 102 in Montreal, DNS privacy will receive a large focus in the DNSOP, DPRIVE and DNSSD working groups. Given the critical role DNS plays as part of the “public core” of the Internet in linking names and identifiers to IP addresses, the DNS must have stronger security and privacy controls. As part of our Rough Guide to IETF 103, here’s a quick view on what’s happening in the world of DNS.
Note – all times below are Indochina Time (ICT), which is UTC+7.
DNS Operations (DNSOP)
The DNS sessions at IETF 103 start on Monday afternoon from 13:50-15:50 with the DNS Operations (DNSOP) Working Group. As per usual, DNSOP has a packed agenda. The major security/privacy-related drafts include:
- DNS query minimisation – draft-ietf-dnsop-rfc7816bis – Back in 2016, RFC 7816 defined an experimental way to increase DNS privacy and limiting the exposure of DNS query information by simply not sending the entire query all the way up the DNS resolver chain. This new work is to move that RFC 7816 document from being an experiment to being an actual Internet standard.
- Running a DNS root server locally – draft-ietf-dnsop-7706bis – Another way to increase DNS privacy is to not send queries up the DNS resolver chain to the root by running your own local copy of the root DNS servers. Back in 2015, the informational RFC 7706 defined how to do this and specified running it on the “loopback” interface of your local computer. This new work broadens that to allow the local copy to run more generally on local systems. At the recent ICANN 63 meeting in Barcelona, this was discussed as “hyperlocal” copies of the root zone of DNS. Wes Hardaker at ISI also has a site about this effort: https://localroot.isi.edu/ Not only could this increase privacy, but also resiliency of the DNS system. However, it is not without its critics and so there could be a good discussion in Bangkok.
- Serving stale data to increase DNS resiliency – draft-ietf-dnsop-serve-stale – This project is setting up the criteria for when DNS resolvers could continue to use DNS data even after the Time To Live (TTL) expires. Basically, if you can’t reach an authoritative server for some reason, under what conditions could you continue to serve the records you previously retrieved from that server?
If there is time in the session, Paul Hoffman’s draft-hoffman-resolver-associated-doh may come up for discussion. This relates to the somewhat controversial DNS Over HTTPS (DOH), now defined in RFC 8484, that lets an app such as a web browser send DNS queries over HTTPS to a DOH server where the DNS resolution can occur. The controversy with DOH is primarily two points: 1) it lets an application completely bypass local DNS servers and thereby bypass local DNS filtering or restrictions; and 2) the first announced use of DOH was by Mozilla Firefox with a DOH server from Cloudflare. This second point brought concerns about centralization and potential choke points. As more entities have stood up DOH servers, there has been a need to help DOH clients understand which DOH server to use. Paul’s draft provides one such mechanism.
If by some miracle there happens to still be time in the session and there is an open mic, I may see if I can briefly ask the group if there is interest in moving forward the draft that several of us worked on about DNSSEC cryptographic algorithm agility – draft-york-dnsop-deploying-dnssec-crypto-algs . However, given the agenda, I highly doubt there will be an opportunity – it will need to be mailing list activity.
DNS PRIVate Exchange (DPRIVE)
The DPRIVE working group meets Wednesday morning from 09:00-11:00 ICT. This meeting at IETF 103 is primarily focused on the discussion about how to add privacy to the communication between a DNS recursive resolver and the authoritative DNS server for a given domain. Specifically they will spend about 30 minutes on the “user perspective” of DNS privacy and a full hour on the “authoritative and recursive perspective” as the working group looks at whether to expand its work to increase the privacy of even more elements of the DNS infrastructure
Extensions for Scalable DNS Service Discovery (DNSSD)
Privacy will also get attention at the DNSSD Working Group on Thursday afternoon from 13:50-15:50 ICT. DNSSD focuses on how to make device discovery easier across multiple networks. For instance, helping you find available printers on not just your own network, but also on other networks to which your network is connected. However in doing so the current mechanisms expose a great deal of information.
The working group had a lengthy discussion at IETF 102 in Montreal about DNS privacy – and are planning for a significant 50 minute discussion block here at IETF 103 in Bangkok.
DNSSEC Coordination informal breakfast meeting
As a final note, on Friday morning we may try an informal gathering of people involved with DNSSEC. We’ve done this at many of the IETF meetings over the past few years and it’s been a good way to connect and talk about various projects. This time we are not sure yet because with the formal meetings ending on Thursday, many people may be traveling home on Firday. We’re not sure of the location and time yet (and we are not sure if it will involve food or just be a meeting). If you would like to join us, please drop me an email or join the dnssec-coord mailing list.
Other Working Groups
DANE and DNSSEC will also appear in the TLS Working Group’s meeting on Wednesday. The draft-ietf-tls-dnssec-chain-extension will be presented as a potential way to make DANE work faster by allowing both DANE and DNSSEC records to be transmitted in a single exchange, thus reducing the time involved with DANE transactions. There has been a lengthy discussion on the TLS list and the chairs are scheduling 55 minutes for this discussion.
Given the key role DNS plays in the Internet in general, you can also expect DNS to appear in other groups throughout the week.
P.S. For more information about DNSSEC and DANE and how you can get them deployed for your networks and domains, please see our Deploy360 site:
- http://www.internetsociety.org/deploy360/dnssec/
- http://www.internetsociety.org/deploy360/resources/dane/
Relevant Working Groups at IETF 103:
DNSOP (DNS Operations) WG
Monday, 5 November 2018, 13:50-15:50 ICT, Chitlada 1
Agenda: https://datatracker.ietf.org/meeting/103/agenda/dnsop/
Documents: https://datatracker.ietf.org/wg/dnsop/
Charter: http://tools.ietf.org/wg/dnsop/charters/
DPRIVE (DNS PRIVate Exchange) WG
Wednesday, 7 November 2018, 09:00-11:00 ICT, Meeting 1
Agenda: https://datatracker.ietf.org/meeting/103/agenda/dprive/
Documents: https://datatracker.ietf.org/wg/dprive/
Charter: http://tools.ietf.org/wg/dprive/charters/
DNSSD (Extensions for Scalable DNS Service Discovery) WG
Thursday, 8 November 2018, 13:50-15:50 ICT, Meeting 2
Agenda: https://datatracker.ietf.org/meeting/103/agenda/dnssd/
Documents: https://datatracker.ietf.org/wg/dnssd/
Charter: http://tools.ietf.org/wg/dnssd/charters/
Follow Us
It will be a busy week in Bangkok, and whether you plan to be there or join remotely, there’s much to monitor. Follow us on the Internet Society blog, Twitter, or Facebook using #IETF103 to keep up with the latest news.
The post Rough Guide to IETF 103: DNSSEC, DNS Security and DNS Privacy appeared first on Internet Society.
Oct 29
Internet Society Seeks Nominations for 2019 Board of Trustees (Featured Blog)
Are you passionate about ensuring the Internet remains open, globally-connected, secure and trustworthy - for everyone? Do you have experience in Internet standards, development or public policy? If so, please consider applying for one of the open seats on the Internet Society Board of Trustees. The Board of Trustees provides strategic direction, inspiration, and oversight to advance the Society's mission. More...
Oct 29
Internet Society Seeks Nominations for 2019 Board of Trustees (Featured Blog)
Are you passionate about ensuring the Internet remains open, globally-connected, secure and trustworthy - for everyone? Do you have experience in Internet standards, development or public policy? If so, please consider applying for one of the open seats on the Internet Society Board of Trustees. The Board of Trustees provides strategic direction, inspiration, and oversight to advance the Society's mission. More...
Oct 29
Nominations Now Open for 2019 Internet Society Board of Trustees Election
The Internet Society Nominations Committee is now inviting nominations for candidates to serve on the Internet Society Board of Trustees.
In 2019, Internet Society Chapters and the IETF will each select one Trustee, and our Organization Members will select two Trustees. Following an orientation program, all new Trustees will begin 3-year terms commencing with the Internet Society Annual General Meeting in July.
The Board of Trustees provides strategic direction, inspiration, and oversight to advance the Internet Society’s mission of preserving the open, globally-connected, trustworthy and secure Internet for everyone.
If you or someone you know is interested in serving on the Board, please see the official Call for Nominations, additional information, and links to online nomination forms at:
http://www.internetsociety.org/trustees
The nominations period closes at 15:00 UTC on Friday, 14 December 2018.
The post Nominations Now Open for 2019 Internet Society Board of Trustees Election appeared first on Internet Society.
Oct 24
New Internet Draft: Considerations on Internet Consolidation and the Internet Architecture
Are there assumptions about the Internet architecture that no longer hold in a world where larger, more centralized entities provide big parts of the Internet service? If the world changes, the Internet and its technology/architecture may have to match those changes. It appears that level[ing] the playing field for new entrants or small players brings potential benefits. Are there technical solutions that are missing today?
These questions were one of many asked in a new Internet Draft published yesterday by former IETF Chair Jari Arkko on behalf of several Internet Architecture Board (IAB) members with the title “Considerations on Internet Consolidation and the Internet Architecture”:
https://tools.ietf.org/html/draft-arkko-iab-internet-consolidation-00
The draft text is based on the IAB “Consolidation” blog post back in March 2018as well as a new post Jari and Brian Trammell have written for the APNIC and RIPE sites.
The abstract of the Internet Draft is:
Many of us have held a vision of the Internet as the ultimate distributed platform that allows communication, the provision of services, and competition from any corner of the world. But as the Internet has matured, it seems to also feed the creation of large, centralised entities in many areas. This phenomenon could be looked at from many different angles, but this memo considers the topic from the perspective of how available technology and Internet architecture drives different market directions.
The document discusses different aspects of consolidation including economic and technical factors. It ends with a section 3, “Actions,” that lists these questions and comments for discussion:
- Are there assumptions about the Internet architecture that no longer hold in a world where larger, more centralised entities provide big parts of the Internet service? If the world changes, the Internet and its technology/architecture may have to match those changes. It appears that level the playing field for new entrants or small players brings potential benefits. Are there technical solutions that are missing today?
- Assuming that one does not wish for regulation, technologies that support distributed architectures, open source implementations of currently centralised network functions, or help increase user’s control can be beneficial. Federation, for example, would help enable distributed services in situations where smaller entities would like to collaborate.
- Similarly, in an asymmetric power balance between users and services, tools that enable the user to control what information is provided to a particular service can be very helpful. Some such tools exist, for instance, in the privacy and tracking-prevention modes of popular browsers but why are these modes not the default, and could we develop them further?
- It is also surprising that in the age of software-defined everything, we can program almost anything else except the globally provided, packaged services. Opening up interfaces would allow the building of additional, innovative services, and better match with users’ needs.
- Silver bullets are rare, of course. Internet service markets sometimes fragment rather than cooperate through federation. And the asymmetric power balances are easiest changed with data that is in your control, but it is much harder to change when someone else holds it. Nevertheless, the exploration of solutions to ensure the Internet is kept open for new innovations and in the control of users is very important.
- What IETF topics that should be pursued to address some of the issues around consolidation?
- What measurements relating to the developments centralization or consolidation should be pursued?
- What research – such as distributed Internet architectures – should be driven forward?
These are all excellent questions, many of which have no easy answers. The draft encourages people interested in this topic to join the IAB’s “architecture-discuss” mailing list (open to anyone interested to subscribe) as one place to discuss this. This is all part of the ongoing effort by the IAB to encourage a broader discussion on these changes that have taken place to the way in which the Internet operates.
It is great to see this Internet Draft and I do look forward to the future discussions to see what actions or activities may emerge. It’s a challenging issue. As the draft discusses, there are both positive and negative aspects to consolidation of services – and the tradeoffs are not always clear.
This broader issue of consolidation or centralization has been an area of interest for us at the Internet Society for quite some time, dating back to our “future Internet scenarios” in 2008 and even before. More recently, our Global Internet Report 2017 on the “Paths to Our Digital Future” recognized the concerns – so much so that we decided to focus our next version of the GIR on this specific topic. (Read our 2018 GIR concept note).
Beyond the Global Internet Report, we’ve published articles relating to consolidation – and it’s been a theme emerging in several of our “Future Thinking” posts. I know that we will continue to write and speak about this theme because at its core it is about the future of what we want the Internet to be.
Please do join in these conversations. Share this Internet Draft with others. Share our 2017 Global Internet Report. Engage in the discussions. Help identify what the issues may be – and what solutions might be.
The Internet must be for everyone. Together we can #ShapeTomorrow.
Image credit: a cropped section of a photo by Paul Gilmore on Unsplash
The post New Internet Draft: Considerations on Internet Consolidation and the Internet Architecture appeared first on Internet Society.
Oct 23
Watch Live – DNSSEC Workshop on October 24 at ICANN 63 in Barcelona
What can we learn from recent success of the Root KSK Rollover? What is the status of DNSSEC deployment in parts of Europe – and what lessons have been learned? How can we increase the automation of the DNSSEC “chain of trust”? And what new things are people doing with DANE?
All these topics and more will be discussed at the DNSSEC Workshop at the ICANN 63 meeting in Barcelona, Spain, on Wednesday, October 24, 2018. The session will begin at 9:00 and conclude at 15:00 CEST (UTC+2).
The agenda includes:
- DNSSEC Workshop Introduction, Program, Deployment Around the World – Counts, Counts, Counts
- Panel: DNSSEC Activities
- Includes presenters from these TLDs: .DK, .DE, .CH, .UK, .SE, .IT, .ES, .CZ
- Report on the Execution of the .BR Algorithm Rollover
- Panel: Automating Update of DS records
- Panel: Post KSK Roll? Plan for the Next KSK Roll?
- DANE usage and use cases
- DNSSEC – How Can I Help?
It should be an outstanding session! For those onsite, the workshop will be room 113.
- WATCH LIVE: https://participate.icann.org/bcn63-113
- More info and slides are available from these URLs (ICANN’s online schedule system breaks it up into sections based on breaks and lunch):
- 9:00-10:15 – https://63.schedule.icann.org/meetings/901549
- 10:30-12:00 – https://63.schedule.icann.org/meetings/901554
- 13:30-15:00 – https://63.schedule.icann.org/meetings/901555
Lunch will be served between the second and third sessions.
Thank you to our lunch sponsors: Afilias, CIRA, and SIDN.
Please do join us for a great set of sessions about how we can work together to make the DNS more secure and trusted!
If you would like more information about DNSSEC or DANE, please visit our Start Here page to begin.
Image credit: ICANN
The post Watch Live – DNSSEC Workshop on October 24 at ICANN 63 in Barcelona appeared first on Internet Society.