
Just a guy in Vermont trying to connect all the dots...

Dan York
Author's posts
Oct 05
Video: The DANE Protocol – What It Is And How It Helps Make The Internet More Secure (via DNSSEC and TLS/SSL)
What is the DANE protocol all about? How does it help make the Internet more secure? How does it work with DNSSEC and TLS/SSL certificates? What added security does DANE provide?
In this interview at IETF 84 in Vancouver this summer, I spoke with Warren Kumari, co-chair of the DANE Working Group within the IETF, about all these questions and also what the future holds for DANE:
To learn more about DANE and how to get involved, you can:
- Read the RFCs and other documents associated with DANE
- Understand the DANE working group charter
- Join the DANE mailing list
We will also be updating our page about the DANE protocol with additional resources, tutorials, tools, test sites and more information in the weeks ahead. There are some great tools under development, including plugins for browsers and tools to generate TLSA records.
Oct 05
Today’s VUC Call – Setting Up A Cellular Network In The Desert For Burning Man
Tim recently described the experience in a guest post at TechCrunch: "What We Learned Running A Mobile Network At Burning Man" and on the VUC call will talk more about what he did. The FAQ from the Papa Legba camp at Burning Man makes for quite an interesting read. I'm looking forward to hearing more from Tim... and the call is open for anyone to join in.
You can join the live call via SIP, Skype or the regular old PSTN. There is also an IRC backchannel that gets heavy usage during the call. It will be recorded so you can always listen later.
If you found this post interesting or useful, please consider either:
- following me on Twitter;
- adding me to a circle on Google+;
- subscribing to my email newsletter; or
- subscribing to the RSS feed
Oct 04
DANE Test Sites
The following sites support the DANE protocol by publishing TLSA records. If you are developing software that supports the DANE protocol, you can visit these sites to test your DANE support. Note that we use the term “TLS certificate” here for what is commonly referred to as a “SSL certificate”.
HTTP – Valid TLSA Record With Valid CA-signed TLS Certificate
- https://fedoraproject.org
- https://torproject.org
- https://jhcloos.com/
- https://www.kumari.net/ - Note: the TLS certificate is for “*.kumari.net”, allowing you to test the use of wildcards.
- https://good.dane.verisignlabs.com
The following sites use a valid CA-signed TLS certificate, but the CA is CAcert, a free CA that is not commonly configured in web browsers:
The following site has a valid TLSA record and a valid CA-signed TLS certificate, but the domain is not tied into the global DNSSEC chain-of-trust, i.e. there is no DS record for huque.com in the .COM TLD:
HTTP – Valid TLSA Record With Valid Self-signed TLS Certificate
HTTP – Valid TLSA Record With Invalid CA-signed TLS Certificate
- https://rogue.nohats.ca - TLS certificate has expired
HTTP – Invalid (Broken) TLSA Record
- https://dane-broken.rd.nic.fr/
- https://bad-hash.dane.verisignlabs.com – TLSA record has incorrect hash value but is correctly signed with DNSSEC
- https://bad-params.dane.verisignlabs.com – TLSA record has a correct hash value but incorrect TLSA parameters. It is correctly signed with DNSSEC.
HTTP – Valid TLSA Record With Invalid DNSSEC Signature
- https://bad-sig.dane.verisignlabs.com – Valid TLSA record but the DNSSEC signature is invalid.
SMTP
The following sites support using DANE for email by publishing TLSA records associated with MX records:
- jhcloos.com
- nlnetlabs.nl (for ports 25, 465, 587)
- nlnet.nl (for ports 25, 465, 587)
XMPP / Jabber
The following sites support using DANE for TLS connections to their XMPP/Jabber server:
- jabber.nlnetlabs.nl
Adding More Sites
If you support DANE with your site and would like to add it to this list, please contact us. Eventually, of course, we would like to hope that DANE is so widely deployed that this list of test sites will no longer be needed.
Oct 04
RFC 6698 – The DNS-Based Authentication of Named Entities
For anyone interested in how to better secure the Internet, the DANE protocol (“DNS-Based Authentication of Named Entities“) provides a mechanism for using DNSSEC to specify precisely which SSL/TLS certificate you want people to use to connect to your web server or other Internet service. This provides a mechanism for ensuring that you are in fact using the correct certificate and your connection is not being intercepted by anyone in your network path. DANE is defined in RFC 6698 at:
The abstract is:
Encrypted communication on the Internet often uses Transport Layer Security (TLS), which depends on third parties to certify the keys used. This document improves on that situation by enabling the administrators of domain names to specify the keys used in that domain’s TLS servers. This requires matching improvements in TLS client software, but no change in TLS server software.
Please view our page on the DANE protocol for more information about how the protocol can be used and how it helps make the Internet more secure.
Oct 04
The DANE Protocol – DNS-Based Authentication of Named Entities
If you connect to a website using a “secure” connection over TLS/SSL, how do you know you are using the correct TLS/SSL certificate?
You may see the “lock” icon in your web browser, but are you sure that you are connecting all the way to the website using the correct TLS certificate? It is in fact quite possible – and quite common – for a firewall or other device in your network path to terminate your TLS connection with a website and then re-create a TLS connection from the device to your browser. You think you have a secure, encrypted connection to your bank, for instance, but in fact your connection has been intercepted and the firewall or other device is able to see, and potentially record, all your interaction with the web site.
With DNSSEC now being deployed, a new protocol has emerged called “DANE” (“DNS-Based Authentication of Named Entities“) that allows you to securely specify exactly which TLS/SSL certificate a browser should use to connect to your site. If a web browser supporting DANE detects that it is NOT using the specified certificate, it can warn you that your connection is insecure… even though you see a “lock” icon.
DANE is defined in RFC 6698 and over the next few months we will be adding more tutorials and document to this site to help you understand both how DANE helps make the Internet more secure and also how you can get started either publishing TLSA records for your domain – or using DANE within your application. Note that DANE is not just for websites. People are already looking at how DANE can be used to secure email, VoIP and other web services.
For an explanation of the DANE protocol, watch this interview with Warren Kumari, co-chair of the DANE Working Group within the IETF:
[Additional screencast to be inserted here explaining how DANE works.]
Another good introduction to DANE is an IETF Journal article published in October 2011 titled “DANE: Taking TLS Authentication to the Next Level Using DNSSEC“. In the article, Richard Barnes explains why DANE is needed, outlines how it works, digs into some of the challenges with DANE implementation and provides a good number of links for more information.
Content Providers
[This section will explain to website owners/operators and providers of other services how they can publish TLSA records to make their sites more secure.]
Application Developers
The following libraries are in the process of adding support for the DANE protocol:
- dnspython – the development version of dnspython found on Github has had support for TLSA records added to the code base. This is not yet available in a formal release.
- ldns – an upcoming release of ldns will provide support for DANE (this page will be updated when the release occurs).
Other resources for developers:
- DANE Test Sites – If you are adding DANE support to your application and wish to test out how well it works, the sites on this page are early supporters of the protocol and can be used in your testing.
Getting More Involved
If you would like to get more involved in the development of the DANE protocol and supporting documentation, you can:
- Read the RFCs and other documents associated with DANE
- Understand the DANE working group charter
- Join the DANE mailing list
Oct 02
How Do We Measure DNSSEC Deployment?
 How do we measure the actual deployment of DNSSEC? How can we know how many domain name holders have signed their zones with DNSSEC? How can we find out how many ISPs have deployed DNSSEC-validating resolvers? How do we count how many applications or operating systems have built-in support for DNSSEC validation?
At first glance, some of these would appear to be simple questions to answer – “well, can’t you just count up the number of DS records in a top-level domain?” But the reality is that it’s not quite that simple. There are sites providing DNSSEC deployment statistics and some TLDs are making DNSSEC usage available… but that’s not true across the board. And the validation question is quite difficult due to the distributed and decentralized nature of the Internet. We recently wrote about some work Verisign Labs is undertaking to measure validation, but that work is just beginning.
The APNIC Experiment
So we were delighted to see the post, “Counting DNSSEC” and accompanying presentation from Geoff Huston and George Michaelson at APNIC Labs where they dug into this DNSSEC measurement issue in a unique way. As Geoff writes, they set out to look at these questions:
- How many zones are DNSSEC signed?
- How many DNS queries are DNSSEC-validated?
- How many DNS resolvers are DNSSEC-capable?
- How many users are using DNSSEC-aware DNS resolvers?
But rapidly concluded that these precise questions were difficult to answer – and so they decided to look a bit more broadly at these questions:
- What proportion of DNS resolvers are DNSSEC-capable?
- What proportion of users are using DNSSEC-validating DNS resolvers?
- Where are these users?
Their measurement technique was to use advertisements in web browsers displayed through an advertising network. They used a flash-based ad that made multiple DNS requests without user intervention, i.e. the user didn’t have to click on the ad – just the action of displaying the ad triggered the measurements.
They ran the test from September 10-17, 2012, and observed 57,268 unique IP addresses requesting the DNS records. Some of the conclusions were interesting:
- 4% of DNS resolvers performed DNSSEC validation
- 9% of end-client systems were using a DNSSEC-validating resolver
Their post goes through all this in great detail and provides a much more thorough explanation than I can do here.
They then went on to look at where the users were coming from and provide charts segmenting their data in multiple different ways. They summarized all of this in a presentation to the recent RIPE 65 event complete with charts showing the validation by country. I’d highly recommend you take a look at that presentation as it provides an excellent view into all this data.
As with any survey like this, you can always wonder about the distribution of people seeing the displayed ad. My first thought was that as I browse with Flash disabled by default I would never have triggered their measurement had it been displayed on my screen. Similarly many mobile devices might not execute Flash, notably Apple devices, and so it would miss those users.
But even with those caveats, this is an excellent piece of work as an attempt to perform some basic measurements. Geoff notes at the end of the post that they’ll perform another look at DNSSEC deployment in a few months time, and we’re very much looking forward to seeing what difference they’ll measure in that next look.
What Else Can Be Done?
Beyond this work, we are still thinking a great bit about what else can be measured. For instance, can we as an industry develop:
- a count of registrars supporting DNSSEC by allowing upload of DS records?
- a count (or %) of DNS hosting providers providing automated DNSSEC signing?
- a % of ISPs providing validating name servers?
- a % of signed second-level domains?
On this last point, there are great examples already out there including the PowerDNS stats for .NL and other domains, the Verisign Labs scoreboard for .COM/.NET/.EDU and the NIST statistics for the US Gov’t and industry, but it would be even better if we could aggregate this information and also obtain that information for other TLDs.
How can we best measure the deployment of DNSSEC? It’s an interesting question… do you have any thoughts about other methods and mechanisms?
Oct 02
Slides: How The Hidden Secret of TCP/IP Affects Real-time Communications
Recently at Voip2day + ElastixWorld in Madrid 2012, Olle E Johansson gave a great presentation outlining where we are at with telecom and VoIP in 2012 - and where we need to go! Olle is a long-time, passionate and tireless advocate for the open Internet, IPv6, SIP and standards and interoperability. I've known Olle for years via Asterisk-related issues, via the VUC calls and via work on SIP over IPv6.
This presentation (slides available) really hits a number of key points about where we are at now:
In particular I was struck by his slides 24-28 that strike the same theme I've been writing about across multiple blogs, namely the way we are reversing the "open Internet" trend and retreating back inside walled gardens of messaging:
He goes on to walk through what happened with SIP and how the protocol evolved - and evolved away from interoperability. His conclusion is that we as customers need to take back control, avoid vendor lock-in and demand interoperability.
He also points people over to his "SIP 2012" effort where he is undertaking to compile a list of what really defines "SIP" in 2012, i.e. more than just RFC 3261. (I'll note he's looking for feedback on these ideas.)
All in all an excellent presentation... and yes indeed we all collectively do need to "WAKE UP" and demand better solutions!
If you found this post interesting or useful, please consider either:
- following me on Twitter;
- adding me to a circle on Google+;
- subscribing to my email newsletter; or
- subscribing to the RSS feed
Oct 01
Video from CO ISOC: IPv6: What is it, why do I need it, and how do I get it?
What is IPv6 all about? Why do you need it? How do you get it? These are the questions a recent event hosted by the Colorado (US) chapter of the Internet Society on August 28, 2012, sought to answer. The session began with a keynote by Scott Hogg, Director,Technology Solutions, Global Technology Resources (GTRI) and then was followed by a panel including:
- Jeff Doyle, President, Jeff Doyle and Associates
- Chris Grundemann, Network Architect, CableLabs
- Cricket Liu, VP, Architecture & Technology,Infoblox
- Shannon McFarland, Principal Engineer, Corporate Consulting Engineering Group, Cisco
- Scott Hogg, Director,Technology Solutions, Global Technology Resources (GTRI)
More information and bios of the presenters can be found at: https://coisocipv6.eventbrite.com/
The session itself is available on YouTube and comes in around 1 hour and 46 minutes:
Oct 01
FIR #671 – 10/01/12 – For Immediate Release
Three speeches and an interview are up; no Asia report this week; Quick News: HootSuite introduces internal feature, Quartz magazine launches, Kellogg's swaps snacks for tweets, Twitter launches header image; Ragan promo; News That Fits: CEOs still fearful of social media, activists use Amazon reviews to undermine book, CustomScoop promo, listener comments, Dan York's report, TemboSocial promo, Klout scores for hiring decisions are stupid, answers to Quora question about PR and social media; music from Lit on the Flash; and more.
Sep 28
U.S. White House Website Now On IPv6
Given that the IPv6 mandate for US federal government agencies came from the Obama administration, a few people noted in recent days that the White House website was not available over IPv6 and indeed it was not listed in yesterday’s run of NIST’s list of US government IPv6-enabled sites.
This morning, though, brings the news that www.whitehouse.gov is now accessible over IPv6. A quick “dig aaaa www.whitehouse.gov” shows these results:
;; ANSWER SECTION:
www.whitehouse.gov.    2441    IN    CNAME    www.whitehouse.gov.edgesuite.net.
www.whitehouse.gov.edgesuite.net. 216 IN CNAME    www.eop-edge-lb.akadns.net.
www.eop-edge-lb.akadns.net. 61    IN    CNAME    a1128.dsch.akamai.net.
a1128.dsch.akamai.net.    7    IN    AAAA    2600:1400:a::1743:fa93
a1128.dsch.akamai.net.    7    IN    AAAA    2600:1400:a::1743:fa78
… which indicate that the site is apparently one of the ones that we mentioned yesterday that Akamai would be enabling via IPv6.
A visit to the White House site using the very cool IPvFoo extension for Google Chrome also shows this graphically:
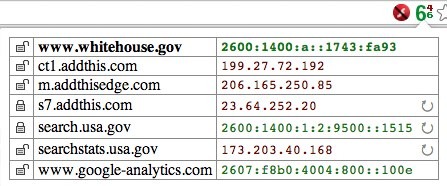
I would note that the image shows the standard challenge of modern websites that they are comprised of many different components that load dynamically, some of which are available over IPv6 and some still only over IPv4. The key point, though, is that www.whitehouse.gov is accessible over IPv6.
Kudos to the White House team and Akamai for making the site available over IPv6. We look forward to seeing how many more US government sites come online throughout today and over the weekend.
Can we help you get started with IPv6?
P.S. If you like the idea of this IPvFoo extension but are a Firefox user, there is a similar add-on called IPvFox.
