
Just a guy in Vermont trying to connect all the dots...

Dan York
Author's posts
Nov 26
Congrats To Keene Ice On The Unanimous Keene City Council Vote!
 CONGRATULATIONS to the team at Keene Ice for the unanimous vote of the Keene City Council to proceed with executing the development and operations agreements between the City of Keene and the Keene Ice organization! This is a huge step forward and means that if the fund-raising all works out we should see a brand new ice arena here in Keene opening as soon as next September – awesome news for those of us who love winter sports!
I was there at the meeting and was delighted to hear Councilor Mitch Greenwald mention during his report about the previous week’s Finance Committee meeting something along the lines of:
“…there was even a guy there from a curling organization… that’s something even we could do [pointing to another councilor] given that we can’t skate…”
EXACTLY!
Curling is a sport that is accessible to all ages… young, old, and everywhere in between. And while you obviously may play better if you are in athletic condition, you certainly don’t need to be. I’ve played on teams with people of all ages and physical conditions. If you can’t bend your knees you can deliver rocks with a special stick. There are even leagues of wheelchair curlers. Pretty much anyone can play curling!
That’s why we want to bring a dedicated curling facility to the Keene region – to provide another winter sport option and to make Keene a true center for winter sports activity!
WILL YOU JOIN WITH US and help us spread the word about bringing curling to the Monadnock region?
P.S. And yes, we are talking to the Keene Ice folks because there does appear to be a place in their plans where they might be able to add a couple of sheets of curling ice! Stay tuned……..
Nov 25
Large-scale Attacks Against VoIP and Videoconferencing Happening Today?
 Are there large-scale attacks happening against VoIP and videoconferencing systems today? Or is it limited to one particular system? In a posting this morning to the VoiceOps mailing list, J. Oquendo wrote:
We have seen a larger than normal, if not, one of the largest attacks against some of our VoIP and video conferencing systems today. Initially, we fielded a report of a “system gone bad” followed by another, then another, and another. This has now carried on into some of our videoconference units (LifeSize).
Because our goal is to get telephony up and running, there was not much we could do via incident response, so I have little to add on attack vectors however, I will state that PBXNSIP has been the primary target, with about a dozen of these being hit pretty hard to the point I’ve had to block all, stop the software and re-start it.
Given that J. Oquendo has been around VoIP security circles for quite a few years now and worked on a number of different projects, I’m inclined to believe his account. Are any of you seeing increased attacks? If so, I think he’d certainly like to hear from you. If you’re not a member of the VoiceOps list, you might also want to join that list as it’s become quite a good resource for people involved in the operations of VoIP systems.
Nov 25
Celebrating 30 Years Of The Domain Name System (DNS) This Month!
 Thirty years ago this month, in November 1983, two RFCs were published that defined the critical Internet service that we now take for granted and use every day – the Domain Name System or more generally just “DNS”. Those two RFCs, authored by Paul Mockapetris, were:
- RFC 882: Domain Names – Concepts and Facilities
- RFC 883: Domain Names – Implementation and Specification
These two RFCs formed the basis for what was to become the DNS system we use today. There was a great amount of discussion in the early 1980′s around how to move beyond the flat naming convention used in the early “ARPA Internet”. Several proposals were out there that make for interesting reading today, including RFC 799, RFC 819 and RFC 830. As Paul Mockapetris relays in a video for the Internet Hall of Fame (IHOF) Internet timeline, his boss at the time, Jon Postel, asked Paul to look at the various ideas and come up with a proposal of his own for how it should work. The result was RFCs 882 and 883.
Four years later, in November 1987, these two original RFCs (882 and 883) were then “obsoleted” by RFC 1034 and RFC 1035 in which Paul updated and expanded the original RFCs based on the experience of those four years in actually implementing DNS. These newer RFCs 1034 and 1035 are still the basis of DNS today, although they have been “updated” many times since, including by the addition of DNSSEC in RFCs 4033, 4034 and 4035.
Today the DNS is a critical part of our Internet infrastructure and is the service guiding us in connecting to all the other services we use across the Internet. We all use DNS all the time every day even though, as Paul Mockapetris wrote earlier this year, we may not even be aware that we are using DNS.
Here at the Deploy360 Programme we are focused on how we collectively can make the DNS more secure using DNS Security Extensions (DNSSEC) and through that how we can make the overall Internet safer and more secure. But as we do that, we do also need to step back and just think about how amazing the overall DNS system is – and how incredibly critical it has become!
Happy 30th anniversary to the DNS! It will be fascinating to see where it goes next!
P.S. Many thanks to Ondřej Surý of NIC.CZ who pointed out this 30-year anniversary today on the dns-operations mailing list.
UPDATE: Our colleague Andrei Robachevsky also provided some commentary in a post, Happy 30th Birthday, DNS!, where he points to some other briefing papers, studies and reports around DNS, and also touches on issues relating to the abuse of DNS.
An audio commentary on this topic is also available:
Nov 25
FIR #731 – 11/25/13 – For Immediate Release
Survey update, interviews coming, AllThingsIC with Rachel Miller debuting, book giveaway contest; Quick News: is BP trolling its critics?, the PR Show in London on Nov. 26, Polyvore drives huge social commerce; Ragan promo; News That Fits: change culture quickly, Michael Netzley's Asia Report, Unilever's social social media campaign, Media Monitoring Minute from CustomScoop, listener comments, KLM uses social media and boosts sales, Dan York's Tech Report, deeplinking in the mobile world; how to comment; music from The House of Jed; and more.
Nov 22
Nov 25th Deadline To Nominate Technical Community Reps for IGF Multistakeholder Advisory Group (MAG) (Featured Blog)
Would you (or someone you know) be interested in representing the "technical community" on the Multistakeholder Advisory Group (MAG) of the Internet Governance Forum (IGF)? If so, the deadline to nominate someone (including yourself) is Monday, November 25, 2013. Under-Secretary-General Wu Hongbo of UNDESA has issued a statement on the Internet Governance Forum (IGF) Multistakeholder Advisory Group (MAG) renewal process for 2014 with the stated aim of rotating one third of the MAG members. More...
Nov 21
TDYR #049 – In Houston, En Route Back To Boston
TDYR #049 - In Houston, En Route Back To Boston by Dan York
Nov 20
Watch Live TODAY The DNSSEC Deployment Workshop At ICANN 48
 As mentioned previously, there is an excellent “DNSSEC Workshop” happening TODAY, November 20, 2013, at the ICANN 48 meeting in Buenos Aires, Argentina. The agenda, slides, and links for remote participation can be found at:
Both and audio and video live stream will be available. The workshop begins today at 9:45 am local time in Argentina, which is 12:45 UTC and 7:45 am US Eastern.
UPDATE: THE WORKSHOP BEGINS AT *8:30am* LOCAL TIME. Or 11:30 UTC / 6:30am US Eastern.
This technical workshop at ICANN meetings continues to be one of the best gatherings of the DNSSEC community and the sessions here again look to be extremely useful and educational. Today’s sessions include:
- DNSSEC Deployment Statistics
- DNSSEC Activities in Latin America
- DNSSEC For The Enterprise
- Guidance For Registrars in Supporting DNSSEC
- DNSSEC Root Key Rollover
- Automated Update of DNSSEC Information
- Operational Realities of Running DNSSEC
- DNSSEC Innovation: DANE Tools and Ideas
The sessions will be recorded if you are unable to watch live, but in watching live you’ll also have a chance to ask questions.
We’re looking forward to a great session today and we’ll be discussing more of what happened there in this blog in the days and weeks ahead.
Nov 19
New Kamailio DNSSEC Module Enables Higher Security For SIP / VoIP
 If you are using voice-over-IP (VoIP), and specifically the Session Initiation Protocol (SIP), how do you know if you are really connecting to the correct SIP server when you make a connection? When you call someone, your SIP server needs to make a connection to the SIP server for the recipient – how is it sure it is reaching the correct server?
As I’ve talked about and written about in the past, one way to help with this is to use DNSSEC to validate that the information received by the SIP server from DNS is in fact accurate. While DNSSEC support in VoIP systems has been somewhat limited to date, the great Kamailio team has added a module that provides DNSSEC support. It will be included in the forthcoming Kamailio 4.1 release (whose development was recently frozen, so it should be available soon), but in the meantime it can be added to Kamailio installations using this tutorial:
The actual module itself can be found at:
This kind of support for DNSSEC within VoIP is great to see and will lead to more secure communications over IP in the future. Plus, getting this kind of DNSSEC support out there now will lay the groundwork for potentially using DANE in the future to secure the certificates used in VoIP communications.
Congrats to the Kamailio team and we look forward to learning more about people using this module in the future!
P.S. See our DNSSEC and DNSSEC Basics pages to learn more about how you can get started with DNSSEC.
Nov 18
DNSSEC Deployment Workshop On Wednesday At ICANN 48 – Live stream available
Interested in learning the current status of DNSSEC deployment? Want to hear case studies from people who have deployed DNSSEC? Would you like to know about some of the latest DNSSEC tools and services? And what the role is of the DANE protocol? All that and more will be discussed this Wednesday, November 20, 2013, at the “DNSSEC Workshop” at the ICANN 48 meeting in Buenos Aires, Argentina. The agenda, slides, and links for remote participation can be found at:
Both and audio and video live stream will be available. The workshop begins at 9:45 am local time in Argentina, which is 12:45 UTC and 7:45 am US Eastern.
UPDATE: The workshop begins at 8:30am local time, which is 11:30am UTC and 6:30am US Eastern.
This technical workshop at ICANN meetings continues to be one of the best gatherings of the DNSSEC community and the sessions here again look to be extremely useful and educational. They include:
- DNSSEC Deployment Statistics
- DNSSEC Activities in Latin America
- DNSSEC For The Enterprise
- Guidance For Registrars in Supporting DNSSEC
- DNSSEC Root Key Rollover
- Automated Update of DNSSEC Information
- Operational Realities of Running DNSSEC
- DNSSEC Innovation: DANE Tools and Ideas
The last of these sessions on DANE will be one where I will be speaking.
The sessions will be recorded if you are unable to watch live… but if you do get a chance to watch live you’ll also be able to ask questions through the web interface. As I mentioned, the slides for the session are all available at that URL above if you’d like to get a head start on seeing what will be discussed.
Do check it out… and get started today with using DNSSEC to make the Internet more secure!
Nov 18
Comcast and Time Warner Show Dramatic Increases In IPv6 Deployment
Great news posted over on the World IPv6 Launch site today – both Comcast and Time Warner Cable in North America have show rather dramatic increases in their deployment of IPv6. Based on the latest published IPv6 measurements, the World IPv6 Launch article included this chart for Comcast:
 And this chart for Time Warner Cable:
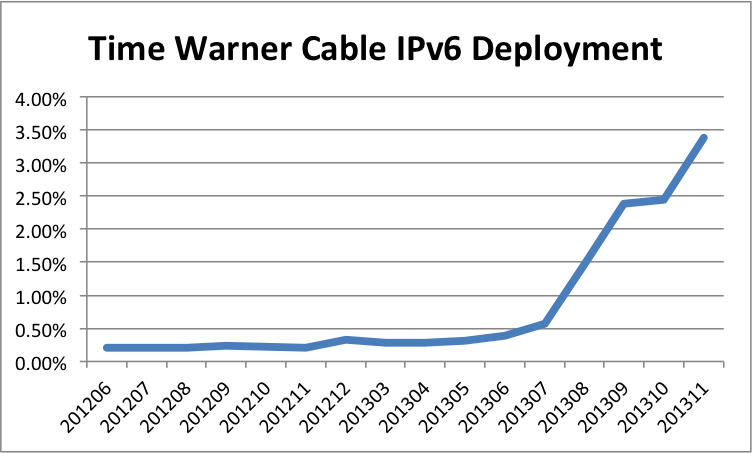 Both of those show a trend definitely going in the right direction! Congrats to the network operation teams at both Internet service providers for making this happen!
Additionally the article pointed out that Google’s IPv6 adoption statistics continue to climb, again showing a very nice upward trend.
All of it goes to show that IPv6 deployment IS happening! If you haven’t deployed IPv6 yet, please do check out our IPv6 resources and let us know how we can help you get connected before you get left behind!
