
Just a guy in Vermont trying to connect all the dots...

Dan York
Author's posts
Apr 10
TDYR 238 – Mind Blown By Looping Of Cello And Double-Necked Guitar
TDYR 238 - Mind Blown By Looping Of Cello And Double-Necked Guitar by Dan York
Apr 09
IANA DNSSEC Root Key Ceremony 21 Streaming Live Today
If you’re interested in the security at the root of DNSSEC, you can watch the IANA DNSSEC Root KSK Ceremony streaming live today – happening right now, in fact – from a data center in Culpeper, Virginia. Just go to:
https://icann.adobeconnect.com/kskceremony
where you can connect to ICANN’s Adobe Connect streaming service. There you can watch as the participants work their way through the 56-page script for today’s key ceremony.
 The key ceremony today began at 1:00pm US EDT (17:00 UTC) and will end at 5:00pm EDT (21:00 UTC).
The key ceremonies are part of the activities performed by the Internet Corporation for Assigned Names and Numbers (ICANN) under its contract to operate the Internet Assigned Numbers Authority (IANA). As explained on the overview page:
Ceremonies are usually conducted four times a year to perform operations using the Root Key Signing Key, and involving Trusted Community Representatives. In a typical ceremony, the KSK is used to sign a set of operational ZSKs that will be used for a three month period to sign the DNS root zone. Other operations that may occur during ceremonies include installing new cryptographic officers, replacing hardware, or generating or replacing a KSK.
This ceremony today is to use the “master” root Key Signing Key (KSK) to generate a set of Zone Signing Keys (ZSKs) that will then be used until the next key ceremony. The “root key” is at the top of the “global chain of trust” that is used to ensure the correct validation of DNSSEC signatures (for more info see “The Two Sides of DNSSEC“) and so it is critical that the security and integrity of this root key be maintained. Ceremonies such as the one today are a part of that effort. If you are interested in learning more, today is a bit of a peek behind the curtain about how all of this happens.
This ceremony will be a bit different from other ones in that they will actually be replacing the Hardware Security Modules (HSMs) that are used to store the actual private key of the Root KSK. This process was explained in detail in a March 2015 blog post: ICANN Announces 2015 Hardware Security Module Replacement Project for the Root Key Signing Key. For those curious, the HSM replacement process starts on page 19 of today’s ceremony script.
Now, granted, occasionally watching people enter commands into a Linux command prompt may not necessarily be as exciting as watching rockets launch…

… but it’s still rather cool that we get to watch the whole process unfold remotely!
And… it’s much more than the command-line operations… you are also getting to see some of the people who hold parts of the keys at the root of DNSSEC do their parts in the actual ceremony. Some of them you may recognize from when we’ve written about them or from some of the articles they written or presentations they’ve made.

You also get to see some of the steps of the process up close:

If you can’t watch it live, it is being recorded and you can always go back and view it.
P.S. If you want to learn more about how to get started with DNSSEC, please visit our “Start Here” page to find resources focused on your type of role or organization.
Apr 07
TDYR 237 – Getting Reacquainted With Microsoft Windows
After many years away in Mac OS X, I recently got reacquainted with Microsoft Windows 7 ... in this episode I talk about what I thought... and how it made me appreciate "less is more" even more!
Apr 07
Deadline of April 10 to Apply For CARIS Workshop on Coordinating Response to Internet Attacks (Featured Blog)
You have just a couple of days to either complete a survey or submit a paper to join the "Coordinating Attack Response at Internet Scale (CARIS)" Workshop happening on June 19, 2015, in Berlin, Germany... If you are interested in helping improve the overall security and resilience of the Internet through increased communication between the groups responding to the large-scale attacks happening on the Internet every day, I would strongly encourage you to apply! More...
Apr 07
46 Years of RFCs (Celebrating The Anniversary of RFC 1)
By way of a tweet from @IETF this morning, it was fun to note that it was 46 years ago today, on April 7, 1969, when the very first "Request for Comments" or "RFC" was issued by Steve Crocker. RFC 1 defined the "IMP software" used in the communication between hosts on the ARPAnet and makes for interesting reading today. Steve was in those days a graduate student at UCLA and 46 years later now serves as the Chairman of the Board of ICANN. Back in 1999, Steve offered some reflections in RFC 2555 on 30 years (at that time) of RFCs that included this bit about how it began:
Dan York
Apr 06
The Hobson & Holtz Report – Podcast #802: April 6, 2015
Thanks to Ragan Communications for their almost 8 years of sponsoring FIR; Gini Dietrich is guest co-host with Shel on the May 4 show while Neville is in Boston;
Quick News:
Collaborate/London intranet workshop from Igloo Software on April 16, alarming declines in social media among Inc 500, good advice in BBC’s updated social media guidelines, companies just aren’t listening to what reporters want from their online newsrooms; the Media Monitoring Minute with CustomScoop.
News That Fits:
Does it make sense to do online Q&As on Reddit, Twitter, etc?; Michael Netzley’s Asia Report: Gushcloud controversy and smear campaigns conducted by blogging cartels; would you use Periscope for employee communication as one CEO did?; listener comments in the FIR Podcast Community on Google+ and via email; The Economist study identifies Gen-narrators who could be effective brand advocates; Dan York’s Tech Report: Turkey blocks social networks, Flickr and the public domain, NASA space image library, and more; Igloo Software promo; the past week on the FIR Podcast Network; with social still treated as an ‘afterthought’ by PR agencies, we offer some advice;
Music from Adri-Ann Ralph; and more.
For Immediate Release: The Hobson and Holtz Report for April 6, 2015: An 87-minute podcast recorded live from Concord, California, USA, and Wokingham, Berkshire, England.
Links to websites, blog posts and other content we discuss in the show are posted as Delicious bookmarks to facilitate your connection with the discussions and sharing of that content.
So, until Monday April 13…
The post The Hobson & Holtz Report – Podcast #802: April 6, 2015 appeared first on FIR Podcast Network.
Apr 06
FIR #802 – 4/6/15 – For Immediate Release
Ragan Communications ends FIR sponsorship; Gini Dietrich to guest co-host on May 4; Quick News: Collaborate London intranet workshop from Igloo Software, alarming social media declines among Inc. 500, BBC's updated social media guidelines, what reporters want from online newsrooms; Media Monitoring Minute from CustomScoop, News That Fits: when not to do online question-and-answer sessions, Michael Netzley's Asia Report, Periscope for internal communication, listener comments, study IDs Gen-narrators as potential brand advocates, Dan York's Tech Report, the last week on the FIR Podcast Network, Igloo Software promo, PR still sees social media as an afterthought; music from Adri-Ann Ralph; and more.
Apr 05
The Tension Between Consumption and Creation of Content (a.k.a. spending time reading Facebook doesn’t help with writing)
Meanwhile, the total number of words I'd written was...
zero.
There is this fundamental tension between consuming content and creating content.
It has nothing directly to do with the Internet, of course. Long before the Internet it was easy to be distracted from writing by TV, radio, books... or just conversations with friends and family, or projects around the house or office.
Distractions have always been numerous... the Internet just does what it does best by removing the middlemen and making it even easier to be distracted.
My friend Donna Papacosta once posted an image on Facebook that I printed out and taped up on my window frame right at eye level that said simply this:
Writing is
3% talent
and
97% not getting distracted
by the Internet
I see that every day when I sit in my home office, with the ever-present reminder that the key word is:
FOCUS
and the need to do that.
Two years ago I wrote a post that took the rather draconian line of "Every Minute You Spend Consuming Content Is A Minute You Are Not Creating Content".
That is, of course, very true. But there is the reality that sometimes we NEED to consume content. Sometimes it is because we are researching something we want to write about. Sometimes it is just simply that we want to relax... that we need to give our minds a break.
I've come to appreciate over many years that there is strong value in stepping away from the creation of content to give yourself a break... and often when you then return to the creating you return refreshed and renewed. Reading a good book or seeing a movie or reading good articles online can often lead to new lines of writing or thinking. There is value in staying up with what friends are doing - and sharing what you are doing.
The trick is trying to find the balance. There is a natural tension between time spent on consumption vs creation. Too much consumption leaves little time for creation. Too much creation can leave you without the benefits of some consumption.
Somewhere in between lies the point we need to achieve.
I don't have the answer... each day I'm trying to find that balance. Some nights like tonight I don't do so well... other days I do.
Focus.
Balance.
If you found this post interesting or useful, please consider either:
- following me on Twitter;
- adding me to a circle on Google+;
- following me on Ello;
- subscribing to my email newsletter; or
- subscribing to the RSS feed.
Apr 01
RFC 7511 – Scenic Routing for IPv6
 Carrying on a grand old April 1 tradition, the IETF today released RFC 7511, Scenic Routing for IPv6. Given the amount of attention in the industry to environmentally-friendly “Green IT”, this RFC aims to help all the poor IPv6 packets that are trapped inside of wires and cables… and instead gives those packets some fresh air!
https://tools.ietf.org/html/rfc7511
Yes, indeed, this new RFC 7511 recommends that packets travel using the RFC 1149 method: “A Standard for the Transmission of IP Datagrams on Avian Carriers“. Either that or over wireless networks… some way that those poor, deprived packets can see some sunlight! 
I did enjoy the little dig at IPv4:
As of the widely known acceptance of the current version of the
Internet Protocol (IPv6), this document only focuses on version 6 and
ignores communication still based on Vintage IP.
Anyway… in the spirit of the day, you may enjoy RFC 7511.
We’ll be back at you tomorrow, when people may actually take things we write more seriously!
Happy April Fools Day!
Mar 31
New DNSSEC Deployment Map Available In Global Internet Maps
Our DNSSEC Deployment Maps are now also available as part of a larger set of Global Internet Maps produced as part of our annual Global Internet Report. My colleague Michael Kende wrote about these new maps earlier this month and explained a bit about them. This new DNSSEC deployment map is rather fun in that it is interactive and you can zoom around and hover over any country to see what stage the country code top-level domain (ccTLD) is at. This map is based off of the 5 stages of DNSSEC deployment that we track as part of the weekly DNSSEC deployment maps we generate. (Click/tap the image to go to the site.)
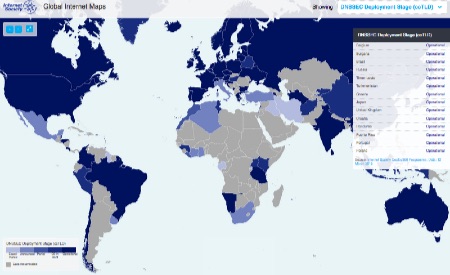
One note of caution – these Global Internet Maps are only updated periodically and so that DNSSEC deployment map will not necessarily be as up-to-date with ccTLDs as the weekly DNSSEC Deployment Maps. The best place to get the most current maps is the archive of the dnssec-maps mailing list. New maps get generated every Monday morning.
However, the Global Internet Map is current now (March 2015) with regard to ccTLDs – and it’s a very nice view of where we need to have more ccTLDs signed with DNSSEC. Please do enjoy using it – while you are there, please do explore all the other maps that are made available. These kind of visualizations are great to see!
The post New DNSSEC Deployment Map Available In Global Internet Maps appeared first on Internet Society.
