
Just a guy in Vermont trying to connect all the dots...

Dan York
Author's posts
Jan 18
TDYR #073 – The Curious Intersection Of Our Time In Ottawa And Tonight’s Continental Cup Of Curling
While watching the live stream of the Continental Cup of Curling tonight, I was pleasantly surprised to learn of a connection between the women's team we were watching and the city of Ottawa and the man who first taught me how to play the sport of curling...
Jan 18
Weekend Project: Set Up An IPv6 Tunnel
 Don’t have IPv6 connectivity to your home or office network? Have you asked your ISP about getting IPv6 and they can’t give you a timeframe?
Don’t despair! One way you can get IPv6 connectivity for your home office is to set up an “IPv6 tunnel” from your network out over your IPv4 Internet connection to an “IPv6 Tunnel Broker” service that will then connect you out to the rest of the IPv6-enabled Internet.
An IPv6 tunnel can work quite well and was in fact what I used for most of two years until my local ISP just recently provided native IPv6 connectivity. The good news, too, is that there are IPv6 tunnel broker services that are available to you for free, operated by companies and organizations that want to expand the use of IPv6.
Two of the most well-known tunnel broker services are:
- Tunnelbroker.net, operated by Hurricane Electric
- SixXS
The general process for both of them is:
- Sign up and register on their website.
- Login to their website.
- Create/request a tunnel.
- Configure your local network to connect to the tunnel.
- Start using IPv6!
Now, step #4 may or may not be a bit involved. Some wireless home routers have a configuration tab somewhere for IPv6 where all you need to do is enter the tunnel information provided by the tunnel broker and away you go! At one point I used an Apple TimeCapsule and was impressed at how easy it was to configure an IPv6 tunnel. There are also some home server/gateway software distributions that also make setting up an IPv6 tunnel easy to do.
To help with this, the SixXS team provides a software client called “AiCCU” and documents the process in “10 easy mini steps to IPv6“. IPv6 advocate Olle Johansson wrote up his experience setting up an IPv6 tunnel through SixXS for his training center.
For Tunnelbroker.net, Hurricane Electric provides configuration information for different operating systems once you login and create a tunnel. They also have tunnelbroker user forums with a wealth of information and tutorials about how to connect from various kinds of systems.
Once you have your IPv6 tunnel connected, you should be able to go to a site like test-ipv6.com and see that you do indeed have IPv6 connectivity! What’s fun then is to install the IPvfoo/IPvfox extension/add-on to either Chrome or Firefox and then as you browse around the web you’ll be able to see what sites you are getting to over your nice new IPv6 connection.
If you’d like more technical information about how IPv6 tunneling services work, you may want to read RFC 7059 that compares different types of IPv6-over-IPv4 tunnel mechanisms.
The cool part of all of this is that you can get IPv6 connectivity while you are waiting for your ISP to join the movement to bring about IPv6 everywhere!
P.S. If any of you want to also write up tutorials of the steps you went through to set up an IPv6 tunnel on your particular hardware or operating system, we’d love to have some more step-by-step tutorials to reference. Please just leave a comment to this post with a link to wherever you post your article. (Or if you don’t have a site to post an article on, drop us a note and we may be able to help you out.)
Jan 17
Watch Live This Weekend – Some Of The Best Curling Teams In The World At Continental Cup 2014
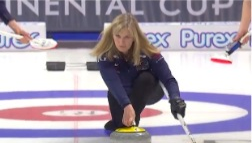 We have an amazing opportunity this weekend (Jan 17-19) to watch some of the best curling teams in the world competing against each other in the “Continental Cup” in Las Vegas. All of it will be streamed LIVE across the Internet at:
http://www.youtube.com/worldcurlingtv
The Continental Cup is a unique format that pits 6 US and Canadian teams in “Team North America” against 6 teams in “Team World” from Scotland, Sweden, Japan and Norway. In contrast to most other curling events that are a series of regular team games, the Continental Cup has team games, singles games, mixed doubles games and ‘skins’ games. The scoring is explained on the event web site.
The remaining games that will be live streamed are (all times US Eastern):
Friday 10 PM – Team
Saturday 12 PM – Mixed Doubles
Saturday 4:30 PM – Team
Saturday 9:30 PM – Team
Sunday 4 PM – Skins
Sunday 9 PM – Skins
According to the US Curling Association web site, NBC Sports Network will also televise two of the Saturday games… although they will be broadcast on Sunday.
The World Curling TV stream on YouTube will be streaming live, of course, and will probably be the best place to see all the action. It should be some outstanding curling so do check it out!
Jan 17
TDYR #072 – Phenomenal Curling Streaming Live From Las Vegas This Weekend
We have a chance to watch some *amazing* curling this weekend streaming live across the Internet as some of the best teams in the world compete in the "Continental Cup 2014" in Las Vegas. The live stream can be found at:
http://www.youtube.com/worldcurlingtv
More info can be found at:
http://monadnockcurling.org/2014/01/17/watch-live-this-weekend-some-of-the-best-curling-teams-in-the-world-at-continental-cup-2014/
http://www.worldcurling.org/world-financial-group-continental-cup-2014
http://www.curling.ca/2014continentalcup-en
http://www.curling.ca/2014continentalcup-en/how-does-the-scoring-work-for-the-continental-cup/
Jan 17
New IETF “openv6″ Mailing List For IPv6 Application Developers
 Do we need an “open interface and a programmable platform to support various IPv6 applications? That is the question posed for a new “openv6″ IETF discussion mailing list announced yesterday. The openv6 list, which is open to anyone to subscribe to, has this description:
This list is to discuss a open interface and a programmable platform to support various IPv6 applications, which may include IPv6 transition technologies, SAVI (Source Address Validation and Traceback), security, data center and etc. This discussion will focus on the problem space, use case and possible protocol extensions. The following questions are listed to be solved via this discussion:
(1) What are the problems and use cases existing in various IPv6 applications, e.g., multiple IPv6 transition technologies co-exist?
(2) How to enable the applications to program the equipment to tunnel IPv6 traffic across an IPv4 data plane?
(3) How this work can be done through a general interface, e.g., to incorporate the transition policies, simplifying the different stages through the transition and guaranteeing that current decisions do not imply a complicated legacy in
the future?(4) How to make the end-to-end configuration of devices: concentrator/CGN, CPE and the provisioning system?
(5) How to extend the existing IETF protocols, e.g., netconf, to support this open interface?
The list is not for forming a new IETF working group (WG). It is at this point purely for discussing this topic. The mailing list archive seems to be empty at the moment (or the link is not correct), but given that the list was just announced yesterday the list owners may be waiting for people to join the list before kicking off discussion. In searching IETF archives I found this recent draft from October 2013, “Problem Statement for Openv6 Scheme,” that may be part of the discussion. I expect we should see more information soon as the discussion begins.
Anyway, if you are an application developer looking to look at how you help your applications work over IPv6 this may be an interesting mailing list to join, if for no other reason than to monitor it and see what work is happening.
I’m looking forward to seeing the discussion begin!
Jan 16
TDYR #071 – A Very Cool Trick To Type Special Characters On A Mac Keyboard
I learned a very cool trick to type special characters while on a Mac... where before to type a "ü" I would press "Alt+u" to get an umlaut and then the "u" key, now I just use what I describe in this episode... VERY cool! (And presumably only for Macs - I don't know if there is a similar trick for Windows.)
Jan 16
W3C/IAB “Strengthening the Internet” Workshop: Deadline Monday to Submit Position Papers (Featured Blog)
How can the open standards organizations of the IETF and W3C "strengthen the Internet" against large-scale pervasive monitoring? That is the topic up for discussion at the "Strengthening the Internet Against Pervasive Monitoring (STRINT)" workshop planned for February 28 and March 1, 2014, and jointly sponsored by the Internet Architecture Board (IAB) and the W3C. The workshop is by invitation-only and has a deadline of Monday, January 20, 2014 (by 11:59 UTC) for submission of either position papers or Internet drafts. More...
Jan 16
Deutsche Telekom IPv6 Traffic Passes 15%, Verizon Wireless IPv6 Traffic Passes 40%!
 The latest World IPv6 Launch measurements are up, and as noted in a blog post by Mat Ford, Deutsche Telekom has shown impressive growth over the past few months with this month’s metrics showing that 15.50%
Also rather significantly you can see in the list that now over 40% of the traffic coming from Verizon Wireless’ network is all going over IPv6! This is all through the fact that Verizon Wireless’ LTE network support IPv6.
The cool part of these World IPv6 Launch measurements is that they are a combination of data collected by Google, Facebook, Yahoo and Akamai. All of those sites are available over both IPv6 and IPv4 and so the sites are measuring the connections that come in to their sites over each protocol.
This shows that as access networks roll out IPv6 availability the content providers are very definitely seeing the connections coming in to their sites over IPv6!
The networks around the world are changing over to IPv6! If you are a website operator or provide other content online, have you thought about how you can make your content available over IPv6?
Jan 16
CircleID: DNS Security Should Be One Of Your Priorities (including DNSSEC)
 We were very pleased to see this recent post over at the CircleID site, “Domain Name System (DNS) Security Should Be One of Your Priorities“, by Rick Rumbarger. He makes a number of great points, particularly about the fact that so many people take DNS for granted and don’t give it the attention they should.
Naturally, given our focus on getting DNSSEC deployed, we were delighted to see his paragraph:
Activate DNSSEC On Your Domain Names – DNSSEC counters cache poisoning attacks by verifying the authenticity of responses received from name servers. It effectively prevents responses from being tampered with, because in practice, signatures are almost impossible to forge without access to the private keys. If your DNS provider is not DNSSEC capable… make a switch.
He’s right! DNSSEC is critical for protecting the integrity of the information you get out of DNS queries. In his paragraph, he talks about the signing of domain names with DNSSEC, but it is important to remember that this is only half the equation with DNSSEC. The other piece you need to do is to enable validation of DNSSEC on your local DNS resolver.
The local validation of DNSSEC information protects the inquiries your computer makes for DNS info, and the signing protects the integrity of your own domain name.
The one point I do take issue with in Rick Rumbarger’s article is his suggestion to outsource ALL your DNS services on both the authoritative side (distributing your domain records) and the recursive resolver side (making inquiries to DNS). On the authoritative side, I agree that outsourcing DNS services can make a whole lot more sense than running your own DNS servers. Most of the DNS hosting companies out there have put a great amount of effort into performance, security, DDoS protection and more – and since they are focused on that can provide better protection and performance than many of us can do ourselves (unless, of course, we operate our own data centers).
However, on the recursive resolver side, I am much more of a fan of having the DNS resolution occur as close to the end user as possible. This is particularly true when you enable DNSSEC validation. Your DNS query is going from the stub resolver on your local computer to the whatever recursive resolvers you have configured in your computer. These are the ”DNS servers” in most operating system network control panels and are often supplied via DHCP to computers on a local network.
The connection between your stub resolver and the recursive resolver you use is typically unencrypted and represents an area where an attacker could inject bogus DNS information. Ideally the connection occurs over a “trusted” network, such as your local area network. If the recursive resolver is on the edge of your local network and is performing DNSSEC validation from that point on, then the attacker would have to somehow get on your local network in order to attack your DNS queries.
If you can’t have a recursive resolver at the edge of your local network, the next best option to me is to use the recursive resolvers at your ISP . You are then only widening the attack surface to be between your local network and that of your ISPs network.
If you can’t do DNSSEC validation at either your local network edge or your ISP, you then do need to go out and use an external recursive resolver that does DNSSEC validation such as Google’s Public DNS. However… the attack surface against your DNS queries has now been expanded to include the entire part of the public Internet that is between your computer and Google’s Public DNS servers (to use the example of Google). An attacker now has a better chance of getting in the middle and injecting false DNS information that goes back to your stub resolver running on your machine.
So for those reasons, I prefer to run the recursive DNS resolver as close to the end user as possible. In the ideal world, the DNSSEC validation might even be performed on the local machine (which can be done today using something like DNSSEC-Trigger) or in the application the user is using.
Outside of that point, I agree with the points Rick Rumbarger raises – and it’s great to see attention being given to this issue of DNS security!
P.S. And to perfectly illustrate one of Rumbarger’s other points about having strong access control for your DNS records there is this post today about how easy it was to get a DNS hosting provider to change DNS records with a simple email message. This is something that DNSSEC will NOT protect against because the DNS hosting provider is changing the actual zone file that would then be encrypted with DNSSEC. It shows again how “DNS security” is really composed of many different layers!
Jan 15
TDYR #070 – Have You Planned Your Own Funeral Yet?
Have you planned your own funeral/memorial service yet? Does anyone know how you would like your death handled? Do you want to be buried? cremated? In this episode I reflect on how a recent experience made me realize how important thinking about these questions can be - as well as sharing that information with others.
